Owned SaaS · Compliance Assessment
Assess and evidence compliance at scale
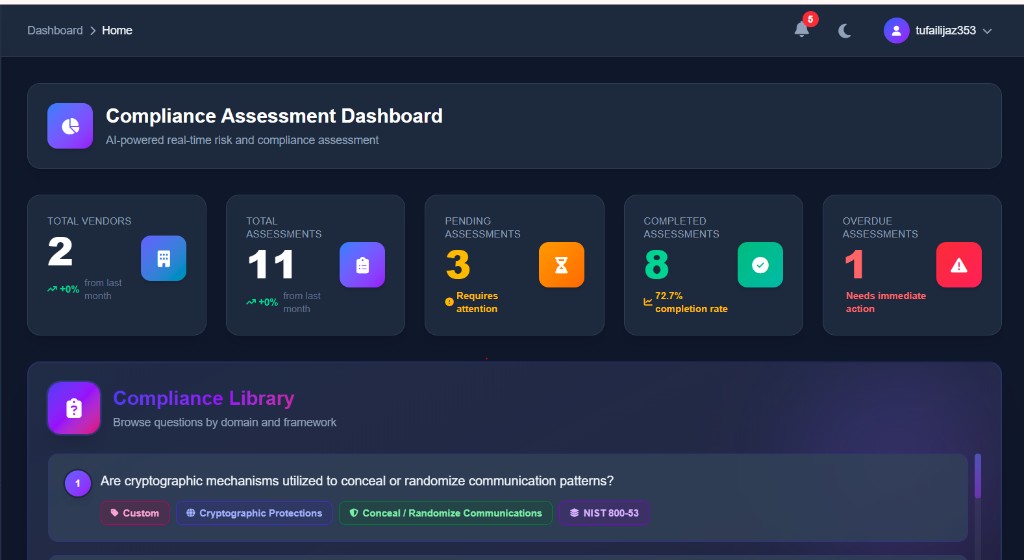
Questionnaires, automated scoring, website security scans, and a compliance library built for enterprise frameworks—so you know whether a counterpart is compliant for a specific project.
Built for security, risk, and procurement teams that need clear compliant vs non-compliant decisions—not another spreadsheet.
- Questionnaire scoring
- Website scans
- 3,000+ controls
- AI-assisted questions
Outcomes
What teams gain with Compliance Assessment
Project-level decisions
Score each engagement as compliant or non-compliant against the work that matters.
Compliant 68%Non-compliant 32%Framework-ready library
Search 3,000+ questions by domain, control, and framework—including NIST, SOC 2, and ISO.
AccessDataOpsVendorClear risk visibility
Pair questionnaire results with website scan findings and a readable risk score.
72 risk
14 findings
Capabilities
Built for the work security teams actually do
Select a capability—the instrument panel on the right shows how that work moves, without repeating the product screenshot stage.
Assessments
Project scoring in motion
Vendors land as compliant, pending, or non-compliant—illustrative sample.
- Compliant 62%
- Pending 20%
- Non-compliant 18%
- Compliant
Acme Cloud
Project assessment
- Pending
Northwind SaaS
Project assessment
- Non-compliant
Orbit Pay
Project assessment
How it works
A clear path from intake to outcome
01
Define the engagement
Select or generate a questionnaire aligned to the project scope and required frameworks.
Templates
12+
02
Collect and scan
Respondents complete questionnaires while optional website scans add technical signal beside questionnaire evidence.
Signals
Scan + Q
03
Score and decide
Auto-score responses, review findings, and record a clear compliant or non-compliant outcome.
Score
72
04
Evidence and reuse
Keep library content, templates, and results ready for the next engagement or audit cycle.
Reuse
Ready
Framework alignment
Illustrative coverage across common enterprise frameworks.
FAQ
Questions we get asked
- What is CixOcean Compliance Assessment?
- Compliance Assessment is an owned SaaS product for assessing and evidencing compliance—with questionnaires, automated scoring, website scans, and a compliance question library.
- Who is Compliance Assessment for?
- Security, risk, and procurement teams in enterprises and regulated organizations—including banks—that need clear compliant vs non-compliant decisions for a specific engagement.
- How does an assessment work?
- Define the engagement, collect questionnaire responses and run website scans, score the results, then keep evidence for reuse on later projects.
- Which frameworks can assessments align to?
- Assessments are built to support common enterprise frameworks such as ISO 27001, NIST, SOC 2, and PCI DSS as assessment content. That does not mean CixOcean itself is certified to those standards.
- How is this different from spreadsheets?
- Structured questionnaires, automated scoring, scan signals, and reusable evidence replace ad-hoc files and one-off audits that are hard to defend over time.
Next step
See Compliance Assessment in your environment
Book a walkthrough with our team, or talk with sales about how this product fits your program.